The Department of Veterans Affairs (VA) technology team needed a faster, more efficient way to approve and deploy new digital services without compromising security.
Rise8 partnered with VA’s technology leadership to integrate security and privacy into the continuous delivery process instead of treating them as a separate step. This approach reduced the authorization process from years to days, improved overall system security posture, and established VA as the first non-DoD agency to achieve continuous Authorization to Operate (cATO).
Working inside VA's enterprise open API program, Rise8 built the platform infrastructure, controls inheritance model, SecRel pipeline, continuous Authorization to Operate (cATO) adherence dashboard, and self-service onboarding automation that made continuous delivery possible. Embedding third-party Security Control Assessors directly into product teams replaced end-of-cycle review with real-time feedback, cutting authorization time from years to days and making VA the first non-DoW agency to achieve cATO. Rise8 also stood up a centralized developer portal, delivered the first application built on the delivery platform, and established a platform enablement team to support every tenant team that followed.
On the Veteran experience side, Rise8 and the VA jointly established an Observability Center of Excellence for VA.gov: a standing capability that watches whether services actually work for Veterans across every team boundary, and proves its work with production data.
Here's a snapshot of what changed after Rise8 got involved with the VA.
The Challenge
VA's enterprise open API program creates a secure portal to VA data for Veterans, VA application development teams, and external partners. These APIs help Veterans access their health records, benefit information, and services, and allow developers to build tools that improve the Veteran experience. The delivery platform is the technical foundation that supports the program, simplifying development, deployment, and operation of critical VA applications. But that platform is one platform inside a much larger and more fragmented VA enterprise, where dozens of systems, teams, and infrastructure layers each own a piece of delivery, while Veterans experience all of it as a single interaction.
A platform in decline
When Rise8 joined the API program, the delivery platform was already under strain. It had passed through successive contractor transitions, and reliability had degraded with each handoff. Developer experience had deteriorated alongside it: onboarding workflows were partially manual, tenant teams lacked guidance on Kubernetes configurations, and deployment pipelines required significant hand-holding to navigate. The result was a platform that slowed down the very teams it was meant to accelerate.
Security approval bottlenecks slowed everything down
While the API program has always followed the NIST Risk Management Framework (RMF) to achieve an Authorization to Operate (ATO), VA's waterfall approach to assessing and authorizing federal systems conflicts with continuous delivery. Those longer cycles produced poor security posture, expensive rework, and delayed value for clinical teams, Veterans, their families, and caregivers.
- ATO took an average of 568 days to complete at the VA, with teams waiting months, sometimes years, before releasing software.
- Security vulnerabilities remained unresolved, with critical issues taking an average of 143 days to be addressed.
- These delays created risk exposure, with 74 Plan of Action and Milestone (POA&M) deficiencies per system in production.
- Teams got stuck in queue when responding to and validating compliance tasks, and security and privacy teams needed longer cycles because they lacked system context.
These delays had direct consequences for Veterans: those with service-connected injuries waited longer for treatment authorizations, benefit claims sat unprocessed, and VA staff were buried in manual paperwork instead of direct Veteran care.
No one owned the Veteran experience across team boundaries
VA.gov is a land of vast information, spread across many teams, systems, and separate monitoring tools. Application teams monitored their own server-side errors, but no one had visibility into whether a Veteran completed a critical task like submitting a claim, sending a secure message, or resuming a saved application. A failure could sit between two teams and pass silently, and leadership lacked a single, trustworthy view of the failures Veterans experienced. Without that view, a small technical glitch could stand between a Veteran and their care or benefits, and no one would know.
The Approach
Rise8 worked in two connected directions across the VA: making continuous delivery secure through the API program, and making the Veteran experience observable through the Observability Center of Excellence. Both operate inside the same VA enterprise, making them complementary.
Building the foundation
As a core member of the platform team, Rise8 architected and delivered the underlying platform infrastructure: deploying an AWS EKS-based Kubernetes environment using Terraform for Infrastructure as Code and ArgoCD for continuous delivery, building a centralized developer portal, designing self-service onboarding automation to reduce tenant time to production, and standing up a platform enablement team to provide white-glove support to application teams building on the platform. Rise8 also delivered the first application built and deployed on the platform, a clinician-facing medication management tool, proving the platform's viability for production workloads. This foundational work established the reliable, developer-friendly infrastructure that made everything else possible.
cATO through the SecRel pipeline
Rise8 transitioned assessment and authorization (A&A) from annual or lower-frequency ATO renewals to a modern Continuous Risk Management Framework (cRMF) aligned with the agile software development lifecycle. We embedded cRMF into the program's agile practices through a shift in culture, process, and technology. We fully digitized the compliance workflow, then automated it through our SecRel pipeline, which attests to security and compliance checks on every code change, including Static Application Security Testing (SAST), Software Composition Analysis (SCA), and container and image scanning.
But cATO doesn't end at the CI/CD pipeline. Continuous monitoring in production flags vulnerabilities approaching SLA deadlines, creating a direct incentive for tenant teams to ship more frequently rather than allow risk to accumulate. The result: tenant deployment frequency shifted from quarterly or longer cycles, to an average of every 25 days.
Automating compliance while raising security
The differentiator is that better security and faster delivery came from the same work, not a trade between them. We eliminated roughly 70% of the security and privacy control response effort for application teams by establishing component-based authorization boundaries, and a controls inheritance model that pre-validated controls at the infrastructure and platform layers. We integrated SD Elements as the countermeasure and compliance-gate system, directly attributing to a reduction in compliance documentation time from the 450-day VA average, down to 80 days.
An internal pilot pairing SD Elements with an AI-assisted workflow cut that to under 40 days, with higher-quality outputs. Assessors returned those countermeasures fewer times compared to those developers completed alone. Rise8 paired that with automated attestation in the pipeline, and embedded technical assessors alongside developers, giving real-time feedback and cybersecurity education instead of end-of-cycle review.
An Observability Center of Excellence across the Veteran journey
Rise8 built the Center of Excellence into a standing capability that watches the Veteran experience across VA.gov, the mobile app, and third-party platforms, across every team boundary. A small team ran continuous watch, eliminated false errors at the source so they stopped appearing entirely, drove issues to closure, and when the owning team could not fix a problem, wrote the fix itself. Every claim carried before-and-after production data, and the team scrapped numbers they couldn't defend. That discipline made the capability credible to VA leadership.
A tech stack built for high availability and continuous delivery
At the infrastructure level, we deployed a CI/CD pipeline on AWS Elastic Kubernetes Service (EKS), Terraform for Infrastructure as Code, and ArgoCD, creating a highly available environment with automated backups, encryption, and storage autoscaling. Observability ran on Datadog with SLA and SLO dashboards and synthetic monitoring. We also authored a custom cATO Playbook to standardize continuous compliance, risk assessment, and security automation across teams. Embedded assessors ran cyber education alongside delivery, giving VA staff the knowledge to operate ongoing authorization themselves rather than depending on a contractor to do it for them.
Enterprise IT in Action
Beyond the API program and the Center of Excellence, Rise8 built and supported additional VA applications on the same enterprise IT foundation, spanning clinical and benefits delivery.
Medication management for clinicians
The first application Rise8 built and deployed on the delivery platform proved the platform's cATO process on a real clinical workload. VA clinicians were spending excessive time parsing medication data in the Computerized Patient Record System (CPRS), the VA's legacy electronic health record platform, leaving less time for direct patient interaction. The application gave Primary Care Physicians a clean graphical view of a patient's active medications and adherence trends, reducing cognitive load during visits. Built using the program's clinical health API, Rise8 went from inception to production in under five months, and maintained a weekly release cadence driven by continuous clinician feedback.
VA.gov notifications
Veterans depend on timely digital communications to manage their healthcare: appointment reminders, visit summaries, and care updates via SMS and email. Rise8 supported the enterprise notification platform, contributing to development, product support, and Tier III engineering operations.
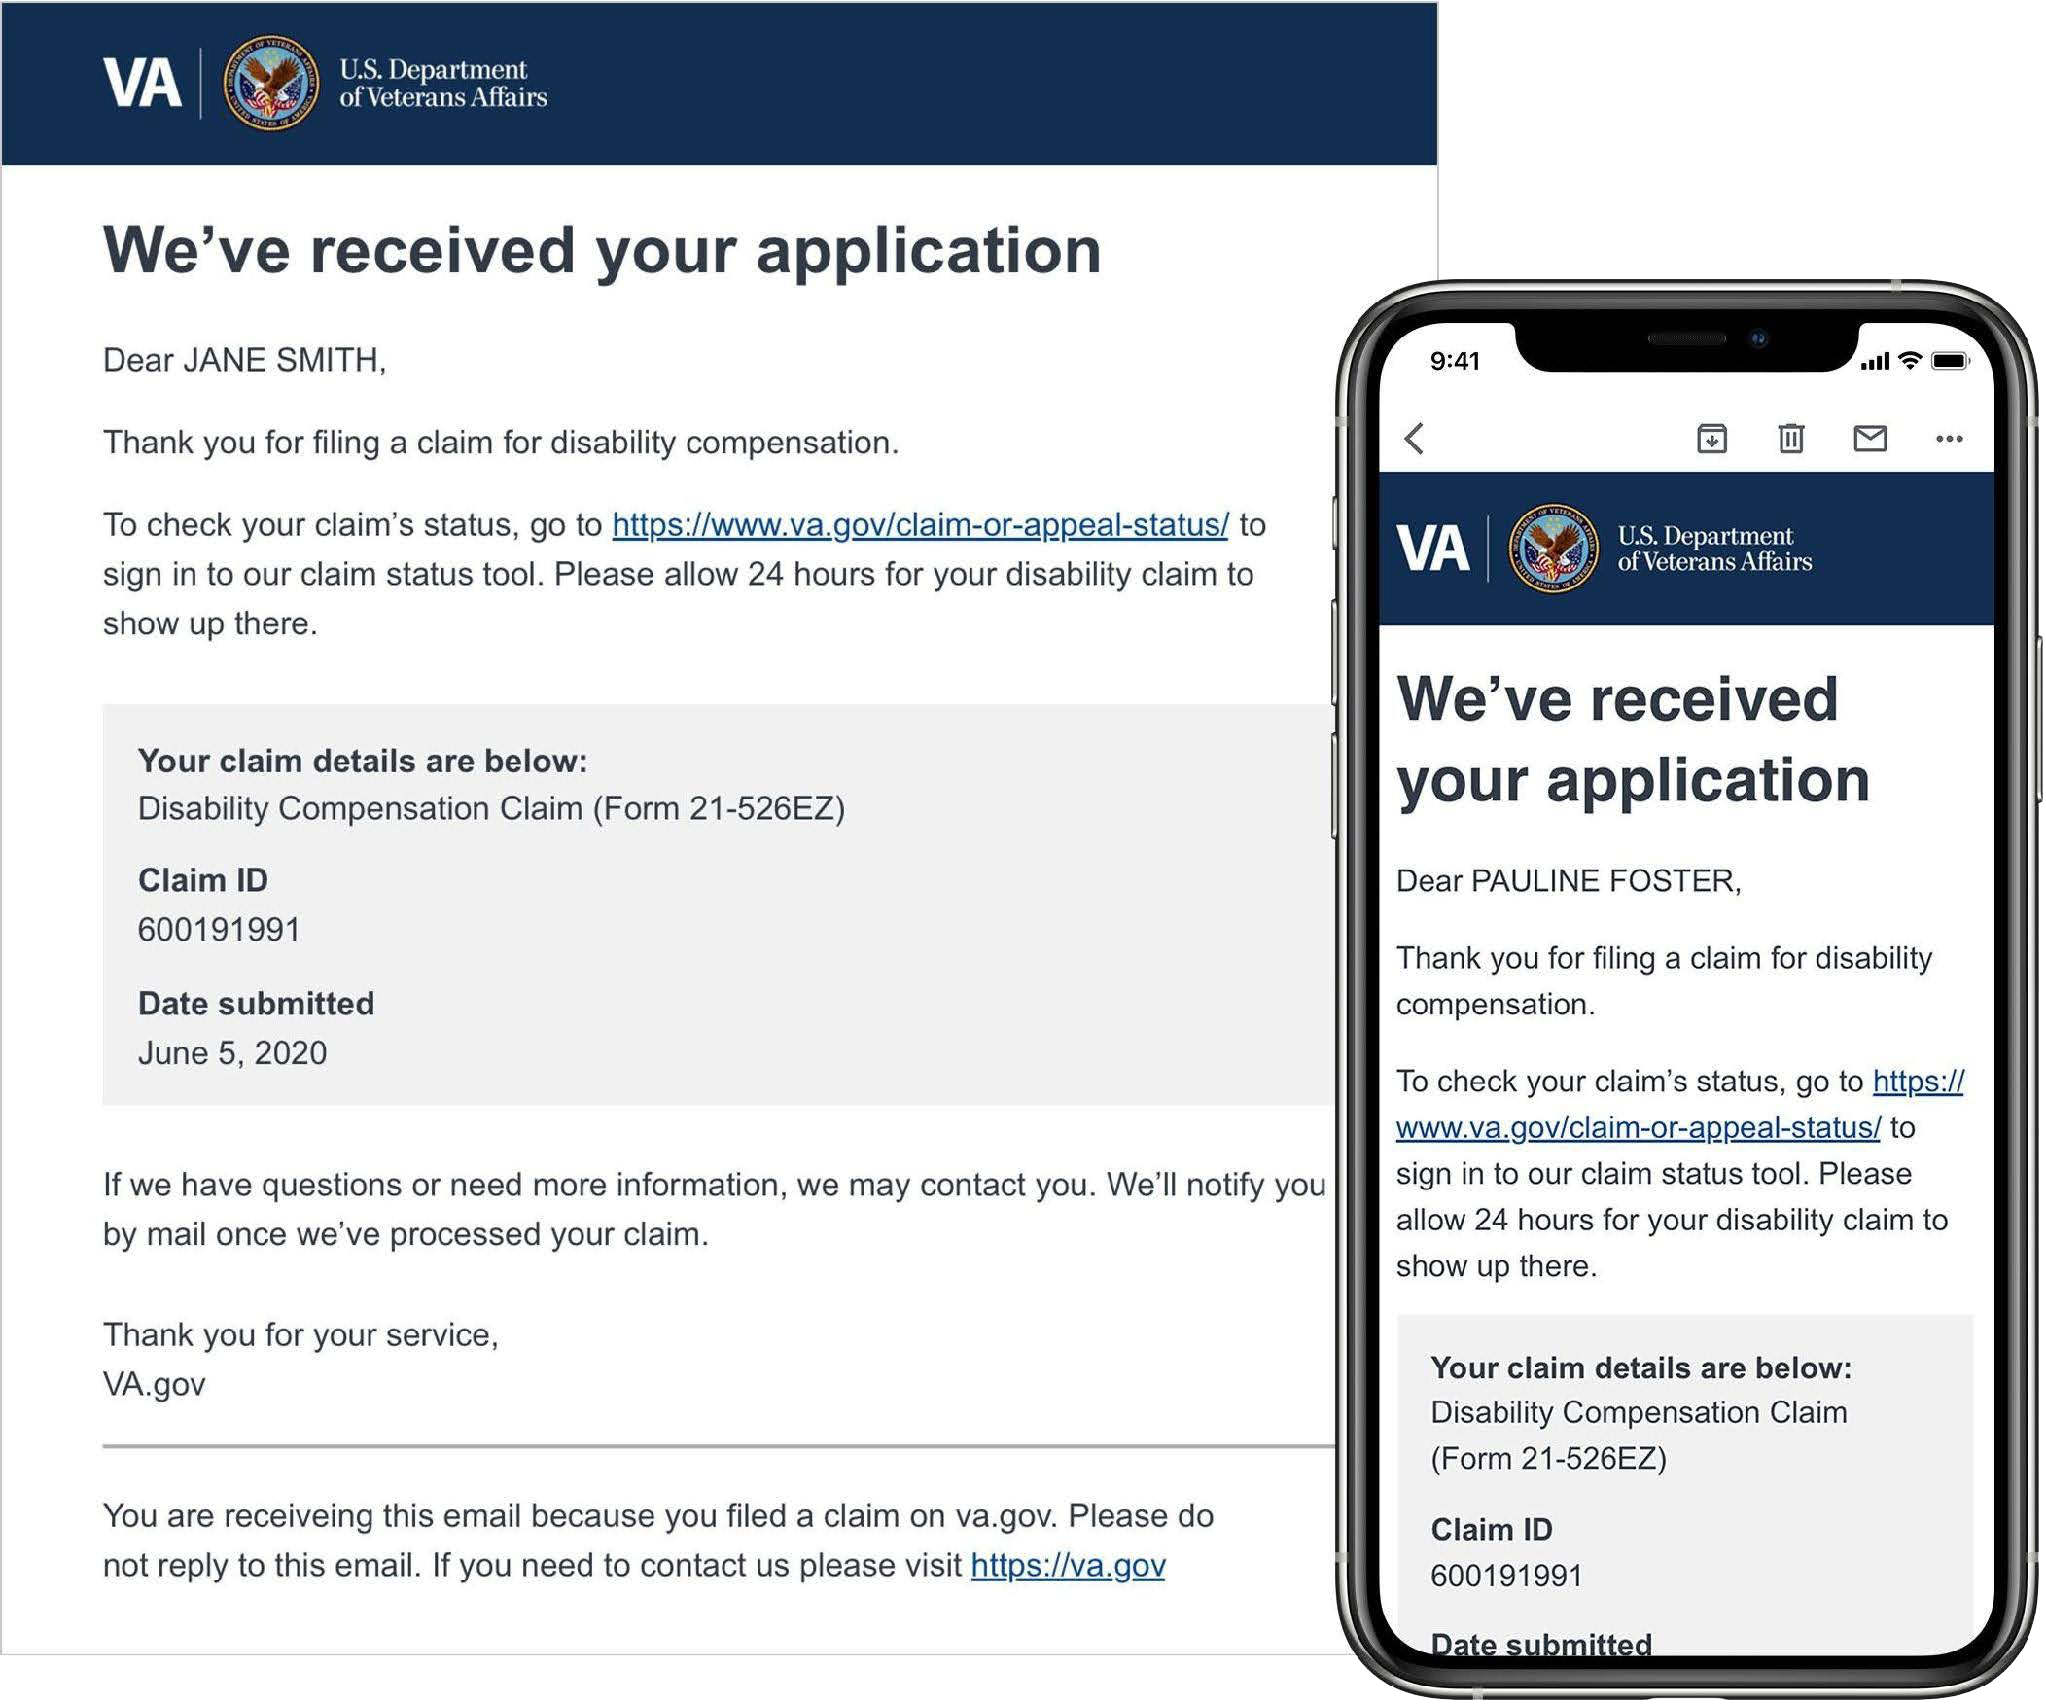
The work included integrating the notification platform and the after-visit summary application with commercial Electronic Health Record (EHR) systems as VA facilities modernized, migrating the notification platform to the VA Enterprise Cloud, and providing engineering-level support to approximately 4,000 VA staff end users. The engagement kept notification delivery running reliably across VA facilities during a significant period of EHR transition.
AI clinical documentation
VA clinicians piloting ambient AI dictation tools faced a critical workflow gap: they had to manually copy AI-generated clinical notes into CPRS, adding friction instead of removing it. Early pilot results showed strong satisfaction from both clinicians and Veterans, but scaling from 10 sites to more than 130 VA Medical Centers required a production-grade integration architecture built for site variability, multi-vendor coordination, and complex VistA/CPRS constraints. Rise8 was awarded the contract to lead that expansion, serving as prime contractor delivering post-MVP enhancements, national rollout support, and Level 2 production operations.
Mission Impact
Rise8 applies the W.K. Kellogg Foundation Logic Model to connect technical execution to mission outcomes.
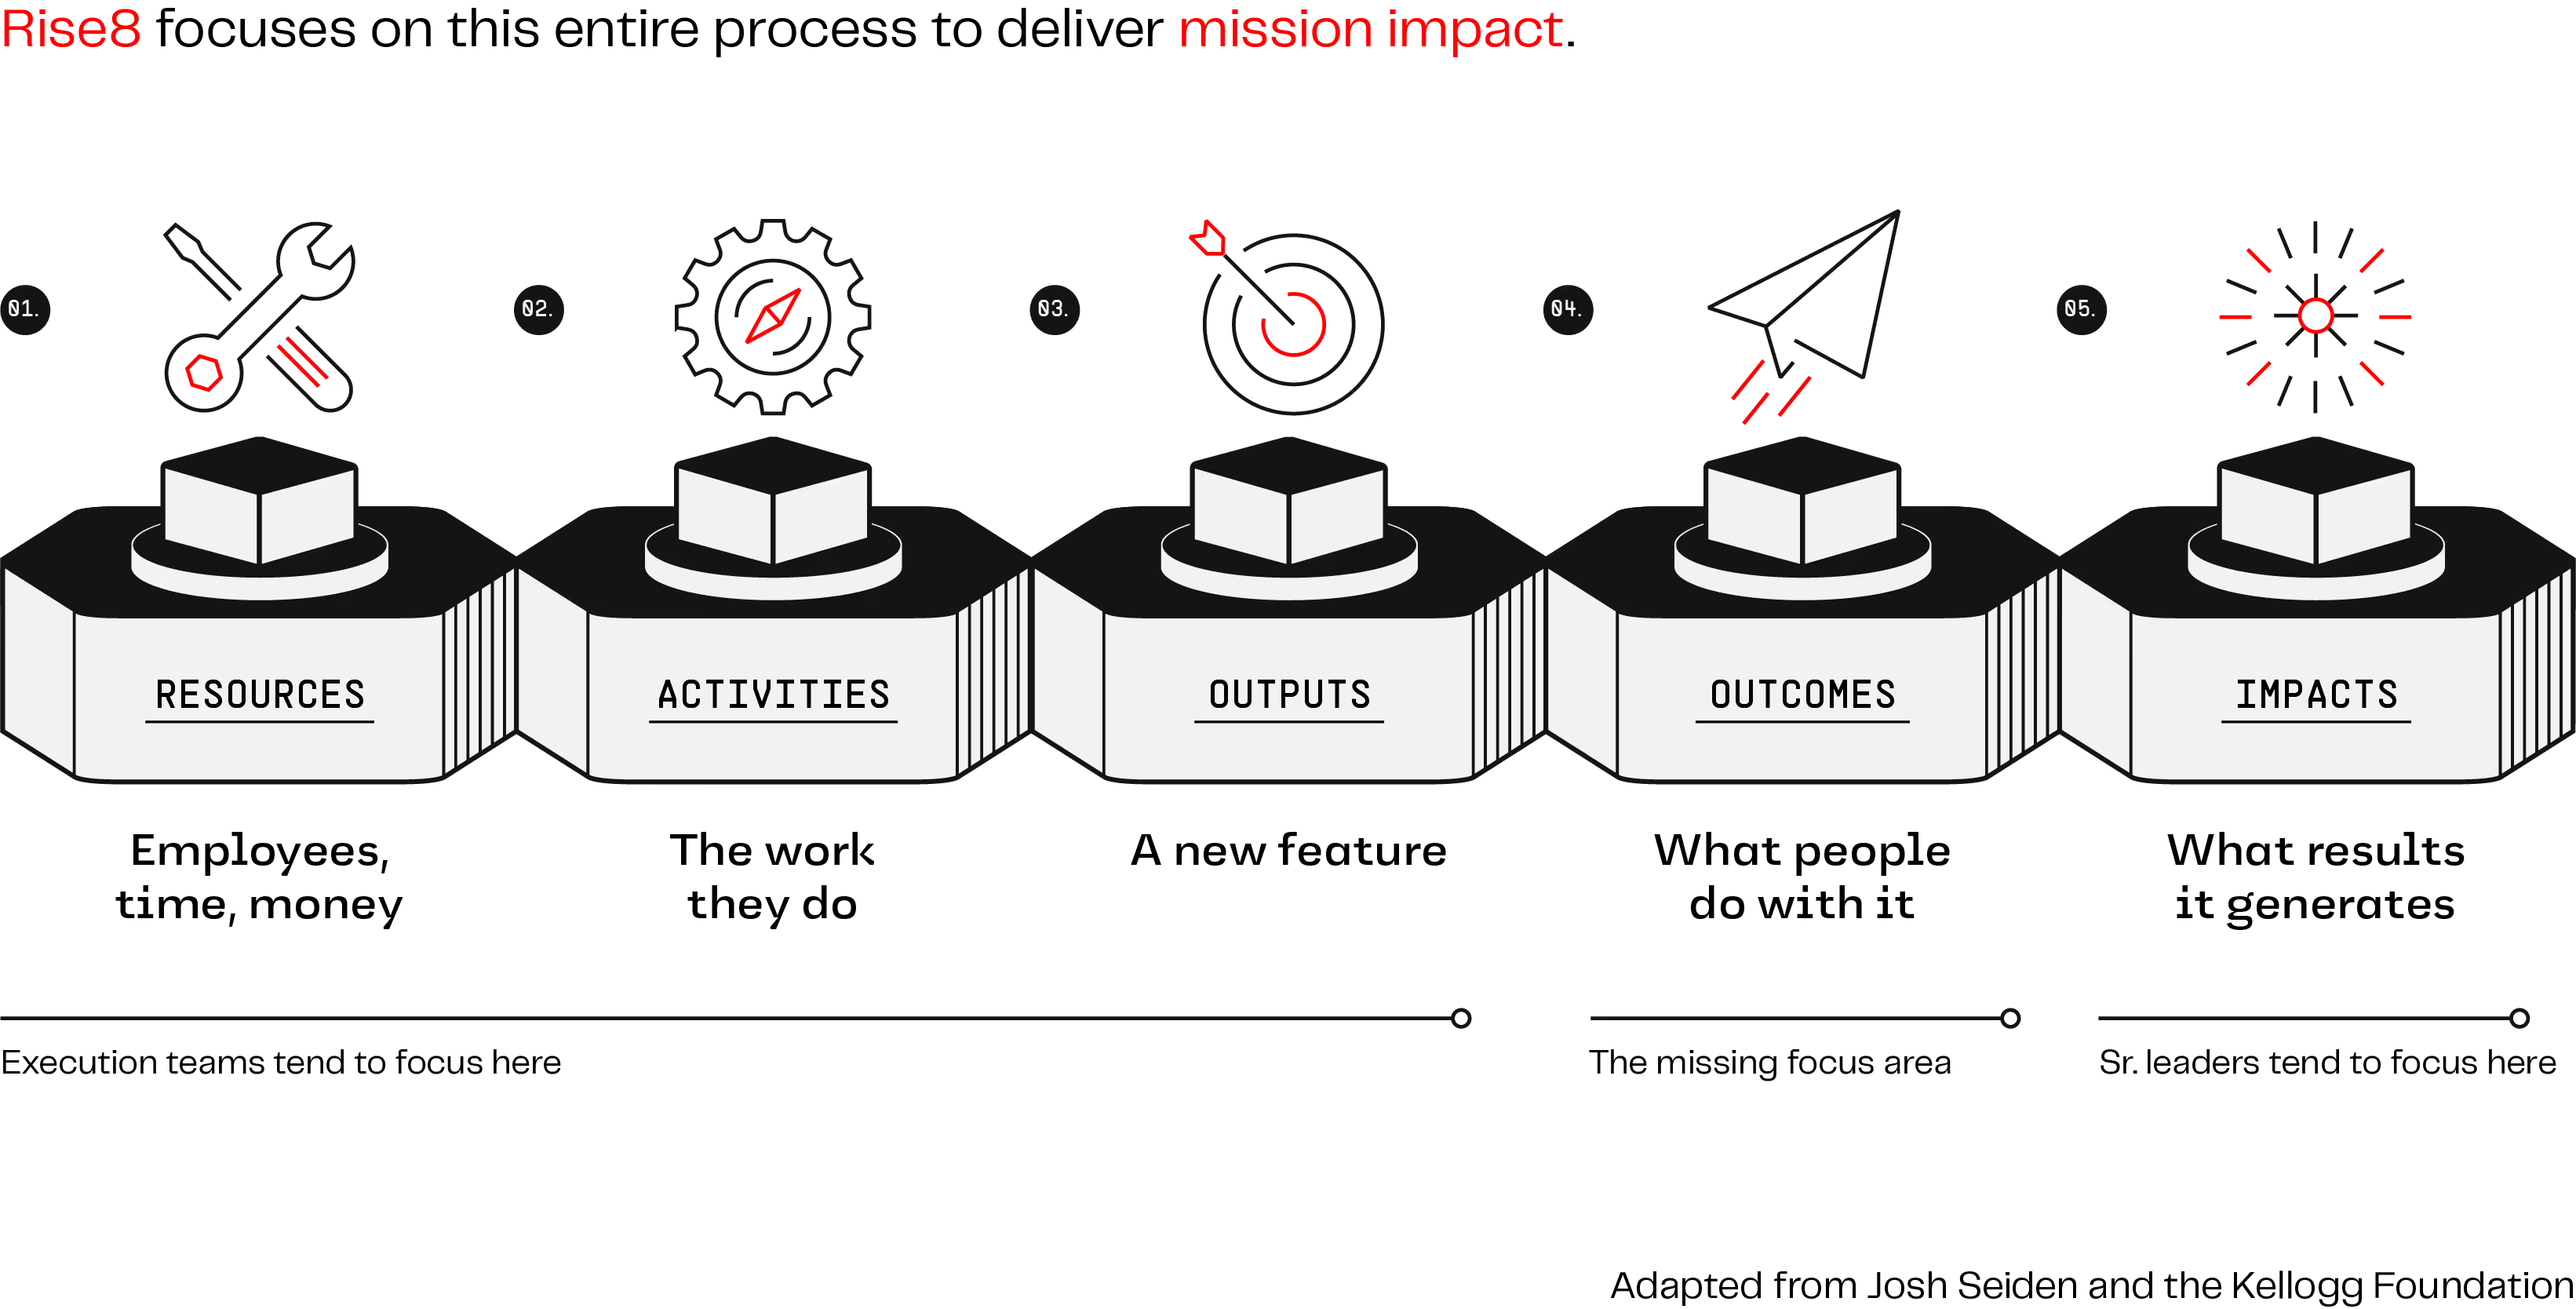
Rise8 applies our Mission O/S methodology, an adaptation of the W.K. Kellogg Foundation Logic Model, to connect technical execution to mission results.
Summary
Rise8 came into VA's enterprise open API program when the platform was already under strain and the authorization process was measured in years. We stabilized the infrastructure, built the developer experience layer, and rewired how security and compliance work, cutting ATO time from 568 days to 87 and making VA the first non-DoD agency to achieve cATO. Better security and faster delivery came from the same work, not a trade between them.
The Observability Center of Excellence gave the VA something it had never had: a standing capability that watches whether services actually work for Veterans across every team boundary, and proves it with production data. In two years of continuous watch, the team closed 1,317 issues and built a safety net catching more than 300,000 failures a week before they passed silently.
Together, these two efforts created a foundation the VA enterprise can build on. Compliance overhead no longer scales with the number of teams. The Veteran experience is no longer invisible across team boundaries. And with the ambient AI clinical documentation expansion underway, the same integration and observability model is now being applied to AI in live clinical workflows at national scale.
Contract Information
This work was completed as part of federal digital modernization initiatives focused on secure software delivery, continuous risk management, and Veteran-facing service reliability, supported by Rise8 across multiple contract vehicles and task orders.
Take the Next Step
Ready to bring continuous delivery to your agency? See how the approach that worked at VA applies to your mission. Talk to our Growth team today.